AWS ทำ OAuth สำหรับ AI Agent แบบ “ขอสิทธิ์จากผู้ใช้จริง” ผ่าน AgentCore
AWS ทำ OAuth สำหรับ AI Agent แบบ “ขอสิทธิ์จากผู้ใช้จริง” ผ่าน AgentCore
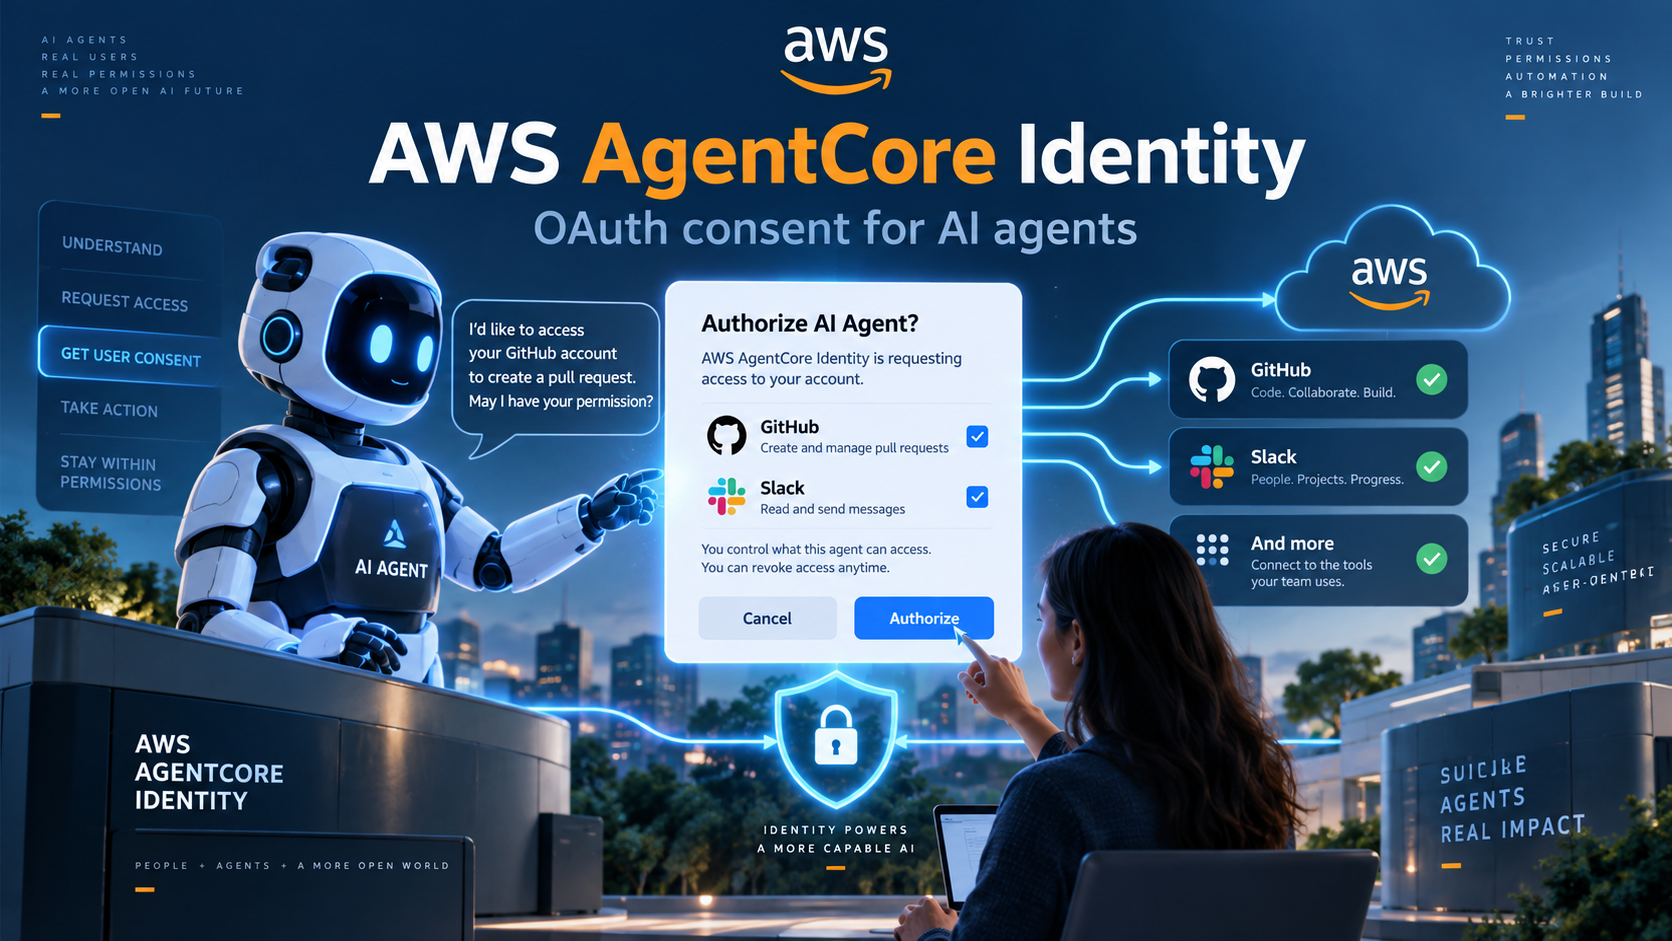
What changed — Amazon Web Services เผยแนวทางใหม่สำหรับ Amazon Bedrock AgentCore Identity เมื่อ 15 กันยายน 2026 เพื่อให้ AI Agent ขอ OAuth authorization จากผู้ใช้ก่อนเข้าถึงบริการอย่าง GitHub หรือ Slack แทนการฝัง token หรือใช้ credential กลางของระบบ Agent.
Why it matters — ปัญหาใหญ่ของ Agent ที่เริ่ม “ลงมือทำงานแทนผู้ใช้” ไม่ใช่แค่ reasoning แต่คือ ใครอนุญาตให้ Agent ทำอะไร ในนามของใคร แนวทางนี้ทำให้สิทธิ์ผูกกับ end user และ OAuth consent โดยตรง จึงเหมาะกับ SaaS/Automation ที่ Agent ต้องเชื่อมหลายบริการภายนอก.
What teams should check — หากกำลังสร้าง Agent ที่เชื่อม GitHub, Slack หรือ SaaS API ควรออกแบบตั้งแต่แรกเรื่อง OAuth scopes, per-user credentials, token lifecycle/revocation และตรวจให้ชัดว่าแต่ละ tool call กำลังทำงานภายใต้ identity ของใคร ไม่ควรให้ Agent ถือ service credential ที่มีสิทธิ์กว้างเกินจำเป็น.
BronzeDev view — Production Agent กำลังเปลี่ยนจากปัญหา “ต่อ API ให้ได้” ไปเป็น “Identity + Permission Architecture” มากขึ้น สำหรับระบบ Agent SaaS ที่เชื่อมหลายแพลตฟอร์ม การแยก credential ต่อผู้ใช้และใช้ least-privilege authorization น่าจะกลายเป็น architecture พื้นฐาน ไม่ใช่ feature เสริม
Primary source: