Amazon EBS Volume Clones Now Cross AWS Account Boundaries
AWS can now copy point-in-time EBS volume clones into another account with optional re-encryption. It is useful for test isolation, provided sharing and key policy are designed carefully.
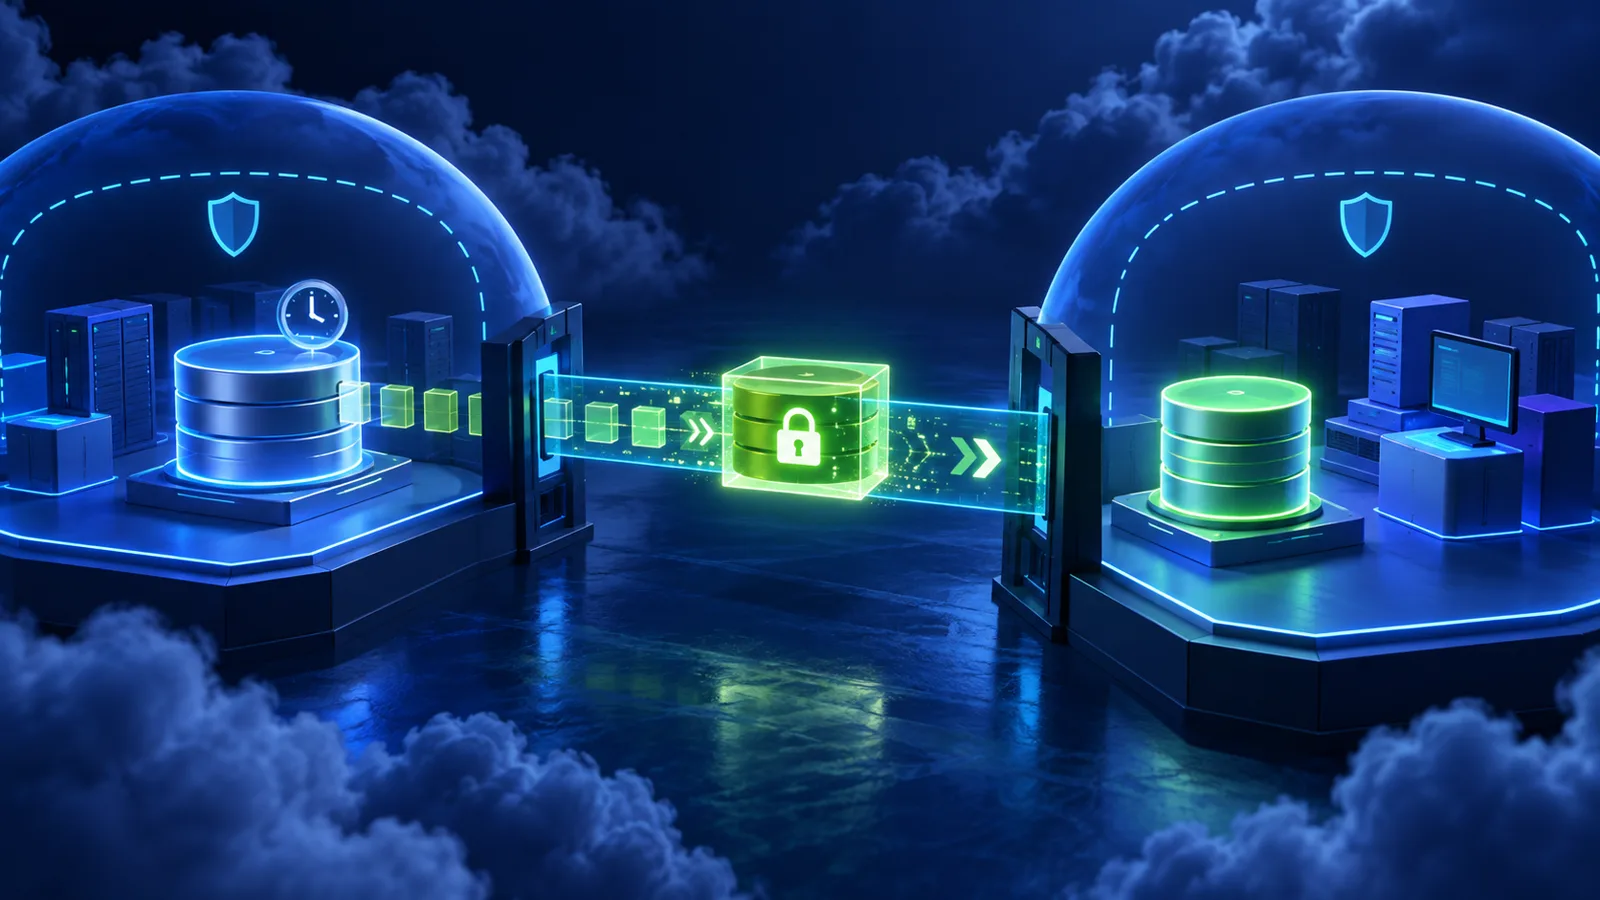
AWS announced cross-account copying for Amazon EBS Volume Clones on September 9, 2026. A source account can share a volume through AWS Resource Access Manager, after which an authorized target account can create its own point-in-time copy.
What changed
EBS Volume Clones already supported instant copies within the same Availability Zone. The extension lets teams place the copy in a separate AWS account and optionally encrypt it with a different customer-managed KMS key in the target account.
AWS says unencrypted volumes and volumes protected with customer-managed keys can be shared. Volumes encrypted with the default AWS-managed key cannot. A customer-managed source key must also be shared when it protects the source volume.
Copy lifecycle events are available through CloudTrail and EventBridge. AWS charges a one-time fee based on volume size in the target account, followed by normal EBS charges. The source and copy must map to the same physical Availability Zone using the Availability Zone ID.
Why it matters
Separate accounts are a strong boundary between production and development. Cross-account clones can refresh realistic test environments without turning the production account into a shared workspace.
The data is still production-derived. A clone may contain customer information, credentials, logs or encryption-sensitive material. Account separation does not replace data minimization and masking.
Controls worth adding
- Share through narrowly scoped RAM resources and remove access after copying.
- Review both volume and KMS key policies.
- Mask or delete sensitive fields before development access.
- Monitor clone initiation and completion events centrally.
- Tag copies with owner, purpose and expiry, then automate cleanup.
- Verify Availability Zone IDs rather than relying on account-specific zone names.
BronzeDev view
The feature makes environment isolation easier, but governance determines whether it is safe. Treat a cloned volume as a new governed dataset with its own access, retention and deletion lifecycle.
Primary source
AWS News Blog: Introducing Amazon EBS Volume Clones across AWS accounts